CRA Article 14 reporting obligations have applied since September 11, 2026—and they are not limited to new products. Manufacturers with existing products on the EU market now need the ability to assess vulnerability impact and respond within the CRA’s reporting timelines.
Many companies see December 11, 2027 as the main deadline for the Cyber Resilience Act (CRA) and assume they still have more than a year to prepare. But that view misses two important points:
The CRA entered into force in late 2024, but its requirements apply in stages:
Since September 11, 2026, when a reportable vulnerability or incident occurs, manufacturers face a staged reporting process:
Reports are submitted through the CRA Single Reporting Platform (SRP).
One common misunderstanding is that manufacturers have 24 hours to fix the vulnerability or complete the entire investigation.
They do not.
The CRA uses staged reporting: manufacturers first report what they know and provide additional information as the investigation progresses.
The real pressure is that the clock starts when the manufacturer becomes aware of the issue, not when a patch is ready or the investigation is complete.
Suppose your security team learns that a third-party component contains a vulnerability and there is reliable evidence that attackers are actively exploiting it.
You immediately need to answer:
If these questions cannot be answered in advance, 24 hours is not enough time to search through codebases, identify affected versions, and find the right decision-makers.
This is why product inventories, Software Bills of Materials (SBOMs), and mappings between products, firmware versions, and software components are no longer just compliance paperwork.
They become the navigation system for vulnerability response.
Without them, even answering the basic question — “Which of our products are affected?” — can become difficult.
Another common assumption is:
“The products we currently sell in Europe were developed years ago. We can simply make our new products CRA-compliant in 2027.”
That is not how the reporting obligation works.
The CRA does provide transitional provisions for products placed on the market before December 11, 2027. In general, those products do not automatically become subject to all CRA requirements unless they undergo a substantial modification after that date.
However, Article 14 reporting obligations are an explicit exception.
Article 69(3) states that the Article 14 obligations apply to all products with digital elements within the scope of the CRA that were placed on the market before December 11, 2027.
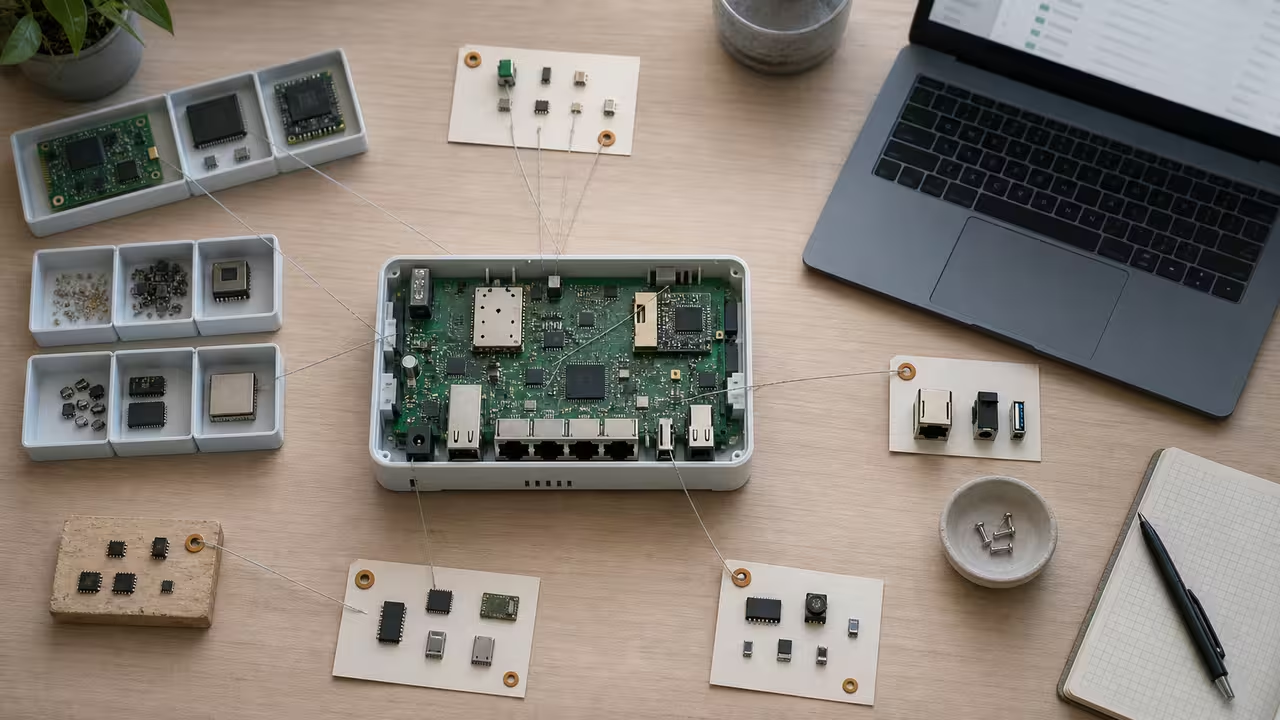
For example, suppose you launched a smart gateway in Europe in 2024. The product was obviously not designed according to CRA requirements. But if a vulnerability in that product meets the Article 14 reporting conditions, the manufacturer is still subject to the reporting process.
This means the immediate impact of the CRA reporting obligations is not limited to new products still under development. It also reaches the installed base of existing products.
Companies do not necessarily need to complete every aspect of their 2027 CRA compliance program immediately.
But three areas should no longer be delayed:
Define:
A tabletop exercise can be useful.
Assume that a third-party component is suddenly found to be actively exploited. Walk through the entire process from the security team receiving the information to submitting the early warning.
The goal is to determine whether the 24-hour response process actually works in practice.
At a minimum, understand:
You do not need to build a complex system on day one.
But you do need a product inventory that can be continuously maintained.
Otherwise, when a vulnerability appears, determining which European products are affected becomes an emergency investigation.
Gradually establish clear relationships between:
Product → Firmware → Third-Party Components → SBOM → Vulnerabilities
When the security team receives new vulnerability information, it should be able to quickly identify potentially affected products and versions instead of asking each engineering team to investigate from scratch.
Once these capabilities are in place, companies can work backward from December 11, 2027 to build their broader CRA compliance roadmap.
That roadmap will involve much more than reporting, including Security by Design, cybersecurity risk assessment, vulnerability handling, security updates, technical documentation, conformity assessment, and lifecycle security management.
CRA penalties can be significant. For certain violations, administrative fines can reach up to €15 million or 2.5% of total worldwide annual turnover for the preceding financial year, whichever is higher.
But for companies selling into Europe, the more immediate pressure may also come from customers and supply chains. CRA readiness and vulnerability response capabilities may increasingly become part of supplier reviews and procurement assessments.
If you focus only on December 2027, it may still feel like there is plenty of time.
But for companies that already have products on the EU market, Article 14 reporting obligations have applied since September 11, 2026.
From now on, when a qualifying actively exploited vulnerability or severe security incident occurs, manufacturers face defined reporting deadlines.
Whether a company can make an initial decision within 24 hours and determine the affected scope within 72 hours depends heavily on whether it already understands the relationships between its products, firmware versions, software components, and vulnerabilities.